The Detection Gap
Screen, Detect and Investigate, Comply & Speak Up | Chapter 1 of 5
Why Financial Crime Compliance Is a Multi-Layer Problem and the Program Required to Address that Problem
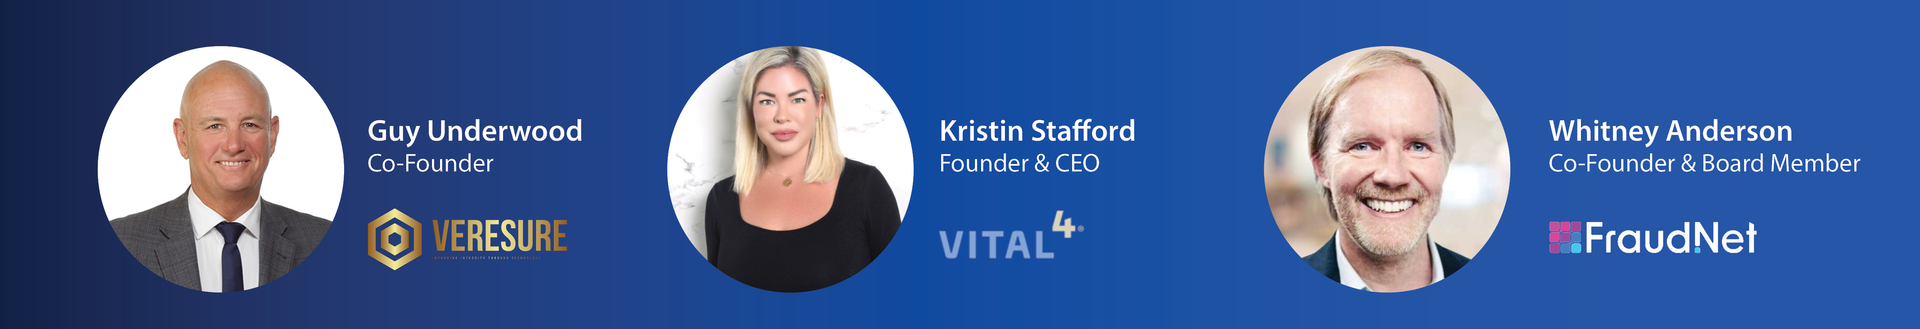
Written in collaboration with Kristin Stafford, Vital4 and Whitney Anderson, FraudNet.
The Financial Services sector believes Australia is facing $4 billion in mortgage fraud — a distributed criminal ecosystem involving AI-generated documents, complicit professionals, and schemes that move through standard compliance frameworks without triggering alerts. With banks and other financial institutions possessing extensive compliance programs involving a range of financial crime solutions, the question is how has mortgage fraud of this scale been able to be committed in Australia.
There is no single answer – however we believe a gap that exists in most regulated entities in Australia right now may hold the key: the gap between screening and detection.
It is estimated that less than 2% of global criminal proceeds are currently detected and seized and with financial services entities around the world being fined $4.3 billion in 2024, it is obvious that regulators are concerned about failures within these entities to detect and prevent financial crime from occurring. It also proves that regulators want more than compliance programs that may “tick all the boxes” required by relevant legislation but are not effective in what they are supposed to do – prevent the movement of illicit funds through the financial system.
Australia's 2026 AML/CTF reforms have forced this reality into the open. From 31 March 2026, existing regulated entities faced strengthened ongoing due diligence and transaction monitoring obligations. From 1 July 2026, accountants, lawyers, real estate agents, and trust and company service providers entered the regime for the first time — a key requirement of the FATF and recognition that these entities are often involved in assisting criminals launder their funds through the financial system. The compliance deadline has arrived. The detection gap hasn't closed.
Why single-layer compliance fails
A key component of any AML programme is screening – of individuals and entities that want to become customers and transactions initiated by those customers as part of their engagement with the organisation Many screening programmes are “point in time” focused and have not been designed to be dynamic to meet changing risk profiles. Whilst this might appear to meet regulatory requirements, it doesn’t mean that the programme is sufficient to reduce the risk of financial crime occurring within an organisation.
Financial crime operates across the full customer lifecycle — in transaction patterns that emerge over months, in entity relationships that don't appear on any watchlist, in behavioural signals that only become visible when data is connected across systems. Screening alone can't see any of that.
Significant penalties (ranging from $700 to $1.3 billion) have been imposed on financial institutions in Australia that have failed – amongst other issues identified by the regulator - to detect and report suspicious activity at scale. Their financial crime programmes were in place, however they failed to detect large scale illegal activity and prevent the laundering of significant amounts of illicit funds.
The three-layer answer
Closing the detection gap requires three capabilities operating together:
- Screen — knowing who an entity is, whether they appear on sanctions, PEP, or adverse media lists, and keeping that knowledge current as their risk profile changes. Vital4 provides this layer: direct-sourced data from over tens of thousands of primary sources, patented AI that cuts false positives, and ongoing monitoring that doesn't stop at onboarding.
- Detect — monitoring behaviour across the entity lifecycle: transaction patterns, network relationships, account anomalies, fraud typologies. FraudNet provides this layer: an entity-first AI platform that resolves 97% fewer false positives than traditional tools and integrates Vital4's screening intelligence directly into its risk decisioning.
- Investigate, Comply & Speak Up — when something surfaces, acting on it properly: conducting investigations and root cause analysis, strengthening the frameworks and controls that failed, fully operationalising compliance requirements and creating a culture where concerns reach decision-makers before they become incidents. Veresure provides this layer: specialist financial crime investigators, regulatory compliance practitioners, and speak-up technology built for environments where standard escalation channels may be compromised.
"Three layers. One framework. No blind spots."
Each layer on its own is valuable. However, without the other two layers, any AML programme will continue to have blind spots. The AUSTRAC reforms have changed what Australian regulated entities must do. The technology to do it properly — as a connected stack rather than three separate vendor relationships — now exists. The remaining question is whether organisations will build the capability or wait for regulators to make the decision for them.
Further Reading
Also in this series:
COMING SOON: Chapter 2 — Screen: How Vital4 closes the data quality gap
COMING SOON: Chapter 3 — Detect: How FraudNet sees what screening misses
COMING SOON: Chapter 4 — Investigate, Comply & Speak Up: When detection isn’t enough | veresure.com
COMING SOON: Chapter 5 — The Integrated Stack: What a capable programme looks like | Vital4 × FraudNet × Veresure
COMING SOON: Download the complete series: vital4.net/austrac-financial-crime
FAQs
Australia’s AML/CTF reforms require more than screening — what exactly changed?
The 2026 reforms strengthened ongoing due diligence and transaction monitoring requirements for existing regulated entities, and brought Tranche 2 professions — lawyers, accountants, real estate agents, and trust and company service providers — into the regime for the first time. The practical shift isn’t just the new entrants. It’s that the compliance floor for everyone moved: onboarding checks alone are no longer sufficient, continuous monitoring is now the expectation, and organisations need to demonstrate they can detect and report suspicious activity, not just screen at intake.
Less than 2% of global criminal proceeds are detected and seized. Is better technology actually going to change that?
Not technology alone — architecture. The 2% figure reflects a systemic gap between what compliance programmes are designed to do and how they actually work in real life to detect and prevent fraudulent behaviour. Screening catches entities at a known point in time against known lists. It doesn’t see behavioural patterns, entity relationships, or fraud typologies that only emerge across the customer lifecycle. Detection and investigation layers change the architecture, not just the tooling. That’s what the three-layer framework addresses: not a better version of what most organisations already have, but the capability they don’t.
I’m a smaller organisation that now has to comply with the AML/CTF Act. How do I develop an effective financial crime programme on a limited budget?
Some of the most significant failures involve major financial institutions that had multi-million dollar budgets to design and implement financial crime programmes. Spending big does not guarantee success and with the right guidance and support during the design and implementation of your financial crime programme, you will stand a better chance of compliant and effective framework. By adopting a risk based approach, your organisation will be able to identify key areas that need to be addressed and adopt technology and support that best meets your needs.